

 WhatsApp
WooCommerce Malware Removal and Hack Recovery



- 5.0 Rating on Clutch, 35 reviews
-
120+ Projects launched
-
90+ PageSpeed score as standard
-
Weekly Demos on a staging site
-
Fixed Scope and price before start
Your store may be compromised
-
01
Browser or Google warning
Chrome shows "Dangerous site" or Google search marks your store. Traffic and ad campaigns drop at once.
-
02
Strange redirects
Visitors from mobile or search land on spam or scam pages, while the store looks fine to you.
-
03
Card data at risk
Customers report fraud after buying, or your payment provider asks questions. A skimmer script on checkout is a common cause.
-
04
Unknown admin users
New administrator accounts, changed passwords or plugins you did not install.
-
05
Spam pages in Google
Thousands of pages in another language appear in search results under your domain.
-
06
Host suspended the account
Your hosting company found malware and took the site offline until it is cleaned.
Hack recovery step by step
-
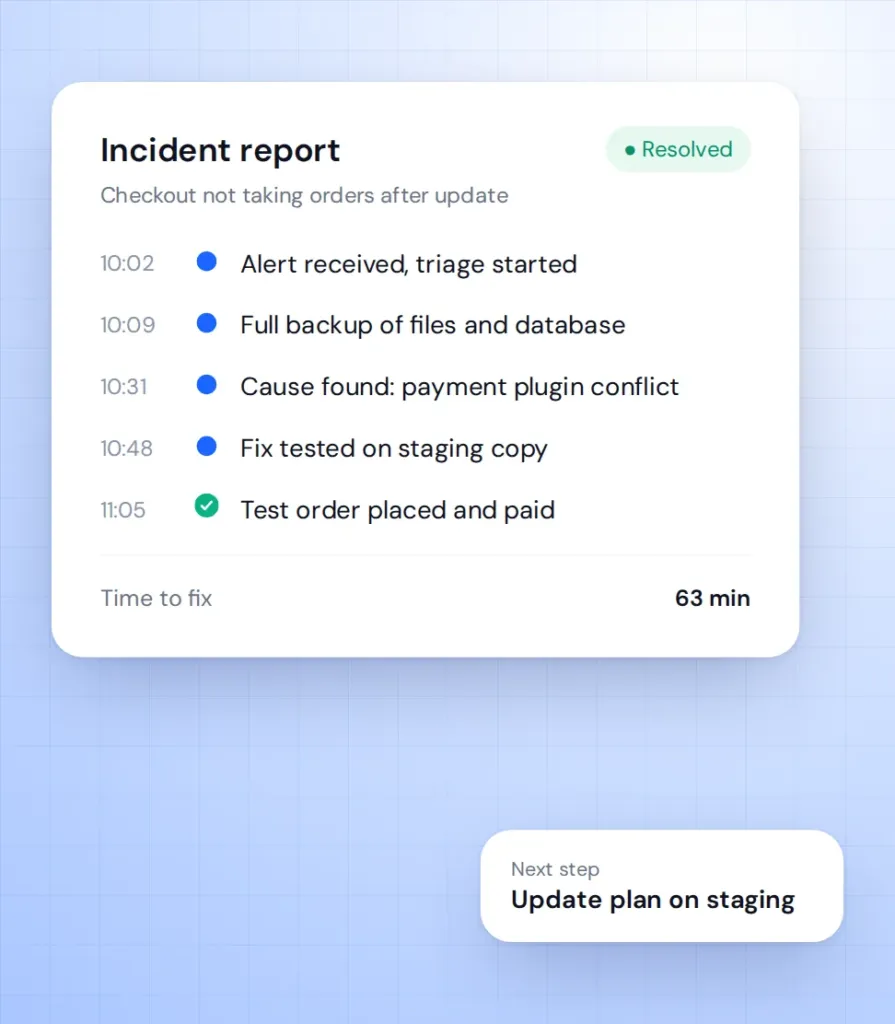
Contain
Backup of the infected site, attacker sessions closed, maintenance page if needed. First hours after access. -
Clean
Files and database cleaned, backdoors removed, clean backup restored where possible. Usually 1-2 days. -
Investigate
Entry point found and patched, checkout scripts checked. 1-3 days depending on the infection. -
Delist
Review request sent to Google Safe Browsing and any other lists. Review time depends on Google, often a few days. -
Harden
Security audit fixes and monitoring on a support plan, so a new attack is caught early.
Hack recovery price guide
The clean-up fee is confirmed after a first look at the infection, before work starts.
-
Clean-up
For stores that need the infection removed and the site back online.
from $450 Usually 1-2 days
- Malware and spam removal
- Backdoor search
- Checkout skimmer check
- Credentials reset
- Google Safe Browsing review request
-
Most popular
Clean-up + hardening
For stores that want to know how attackers got in and close every gap.
from $1,100 Usually 3-7 days
- Everything in Clean-up
- Entry point report
- Security audit of code and server
- Vulnerable plugins updated or replaced
- Login and admin protection
-
Monitoring
For stores that want someone to watch for new threats every month.
from $300/month Care plan
- Malware and file change scans
- Regular updates and backups
- Uptime checks
- Response within 1 business day
Prices are a guide. You get a fixed quote after a free discovery call.
How we clean and secure the store
-
Contain and back up
We copy the infected site for evidence, block attacker access and put up a maintenance page if needed.
-
Clean-up
Core, theme and plugin files compared with clean versions. Injected code, spam pages and bad database entries removed.
-
Entry point and backdoors
We look for how attackers got in: a vulnerable plugin, a leaked password, a weak server. Hidden backdoors are removed so they cannot come back the same way.
-
Checkout skimmer check
Checkout, payment scripts and third-party tags reviewed for code that steals card data.
-
Credentials reset and restore
All admin, hosting, database and API keys changed. Where a clean backup exists and is recent enough, we restore it and bring missing orders back.
-
Blacklist removal and hardening
We request a review from Google Safe Browsing, then close the gaps with a security audit and monitoring.
Learn more
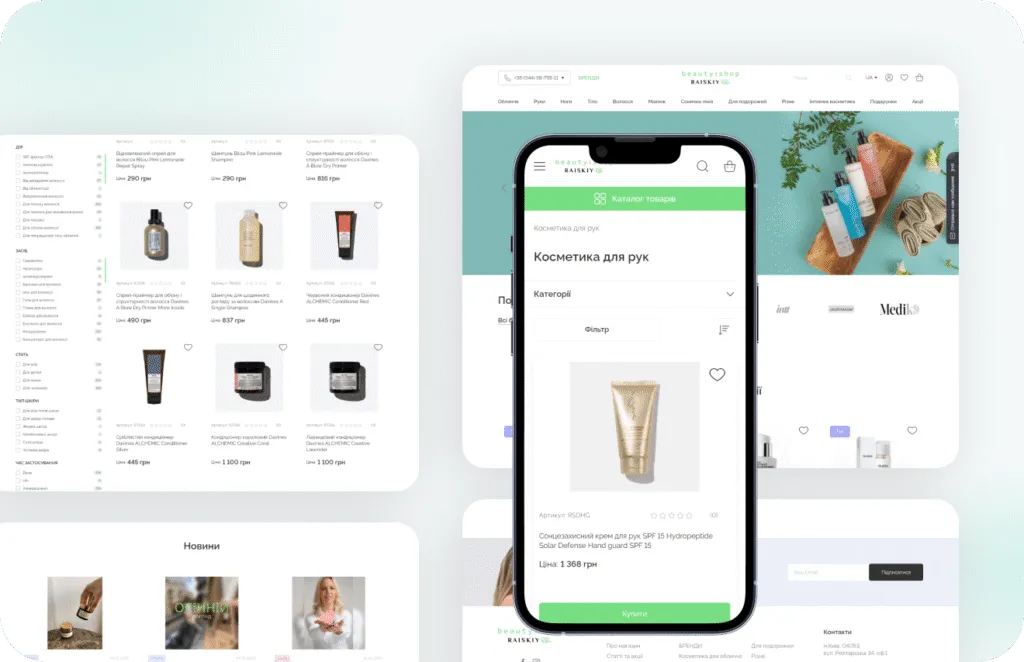
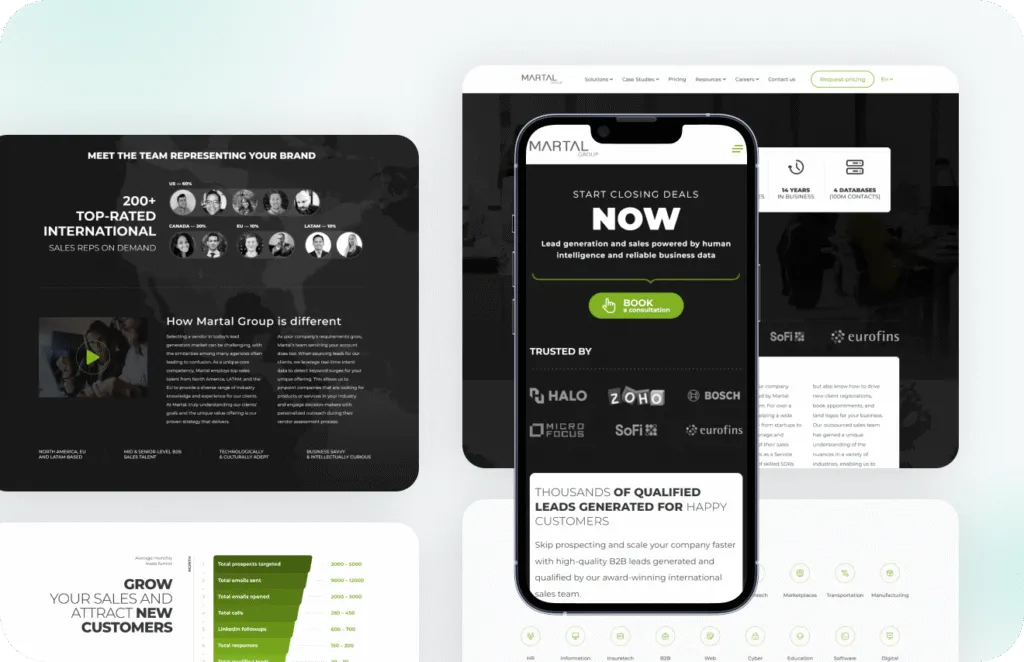
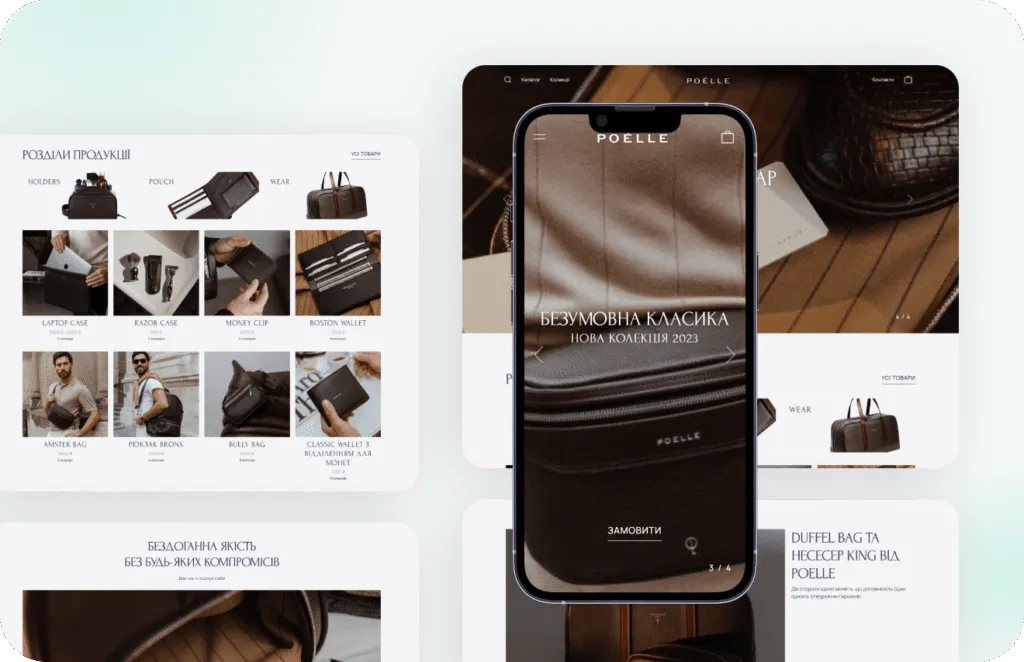
Stores we've built. Results
they've driven.
What our clients say

Why Artilab for WooCommerce malware removal
We know WooCommerce checkout
Root cause, not only clean-up
Honest about limits
Security audit next
Malware removal FAQ
What store owners ask when their site is hacked.
How long does WooCommerce malware removal take?
Most clean-ups take 1-2 days. Finding the entry point and hardening adds a few days, depending on how deep the infection is.
Can you guarantee the store will not be hacked again?
No one can honestly guarantee that. We remove the infection, close the entry point we find, harden the store and set up monitoring to catch new problems early.
Was customer card data stolen?
We check checkout for skimmer code and tell you what we find. If data may be exposed, contact your payment provider; we give you a technical report for that talk.
Will you remove the Google warning?
We clean the site and request a review from Google Safe Browsing. The decision and timing are Google's, but a clean site is normally delisted after review.
Should we restore an old backup ourselves?
Not before you know when the infection started. A backup can already contain the malware, and restoring it can lose recent orders.
Will we lose orders?
We protect order data first. If we restore a backup, we bring newer orders back from the infected copy after cleaning.
