

 WhatsApp
WooCommerce Security Audit



- 5.0 Rating on Clutch, 35 reviews
-
120+ Projects launched
-
90+ PageSpeed score as standard
-
Weekly Demos on a staging site
-
Fixed Scope and price before start
How WooCommerce stores get hacked
-
01
Outdated plugins
Many WordPress breaches start with a known hole in a plugin or theme that was never updated.
-
02
Nulled or abandoned plugins
Pirated premium plugins often carry malware, and abandoned ones never get security fixes.
-
03
Card skimmers at checkout
Injected JavaScript can copy card data on checkout pages without any visible change.
-
04
Weak admin access
Shared admin logins, no two-factor login and old accounts that still have shop manager rights.
-
05
Exposed files and endpoints
Public debug logs, backup files in open folders and XML-RPC left on invite attacks.
-
06
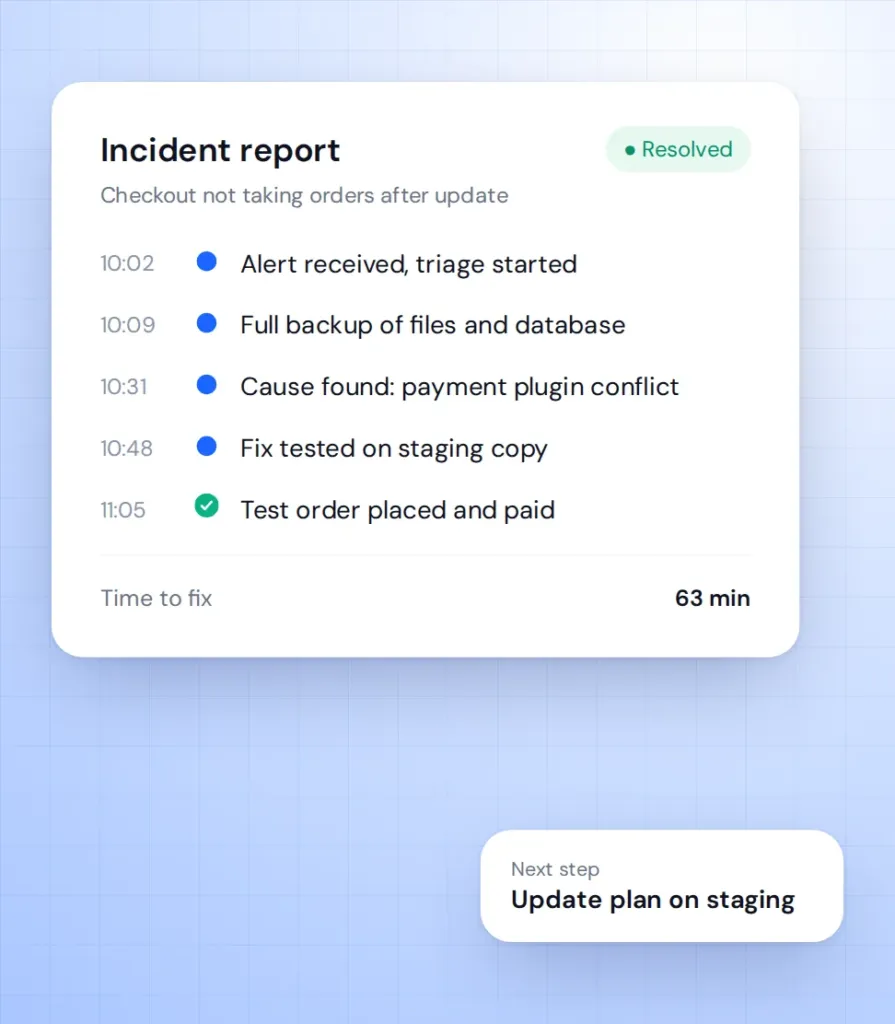
No incident plan
No clean backup, no logs and nobody who knows what to do on the day the site is hacked.
How the audit works
-
Access
You give us read access and a backup, and we set up a staging copy. 1-2 days. -
Scan
Automated scans of plugins, files and server settings, plus a malware check. 2-3 days. -
Manual review
A developer reads custom code and checks settings that scanners miss. 3-5 days. -
Report
You get a plain-language report with each risk, its level and the cost to fix it. -
Fix and retest
If you choose hardening, we fix issues on staging, deploy and run the checks again. 1-2 weeks.
Security audit and fixes
The audit has a fixed price, and fixes are quoted from what it finds.
-
Security audit
For stores that want a clear risk report before deciding on fixes.
from $800 1-2 weeks
- Plugin and theme vulnerability check
- Custom code review
- User and access review
- Server and config check
- Report with risk levels
-
Most popular
Audit and hardening
For stores that want every serious risk found and closed.
from $2,000 2-4 weeks
- Everything in Security audit
- Fixes for high and medium risks
- Firewall and login protection
- Two-factor login for all admins
- Backup restore test
- Retest after fixes
-
Ongoing protection
For stores that want security watched after the audit.
from $250/month Monthly
- Malware and file change scans
- Vulnerability alerts for your plugins
- Tested security updates
- Priority incident response
- Monthly security report
Prices are a guide. You get a fixed quote after a free discovery call.
What the audit covers
-
Plugins and themes
Every plugin and theme checked for known vulnerabilities, abandoned code and nulled copies.
-
Custom code review
Theme and custom plugins reviewed for SQL injection, XSS, missing nonces and unsafe file uploads.
Learn more -
Users and access
Admin and shop manager accounts, passwords, two-factor login and REST API keys reviewed.
-
Checkout and payments
Checkout scripts checked for skimmers, and card handling checked against the PCI DSS rules for your gateway type.
Learn more -
Server and configuration
PHP version, file permissions, wp-config, exposed files, HTTPS and security headers.
-
Backups and recovery
We confirm that off-site backups exist and restore, and write a short incident plan.
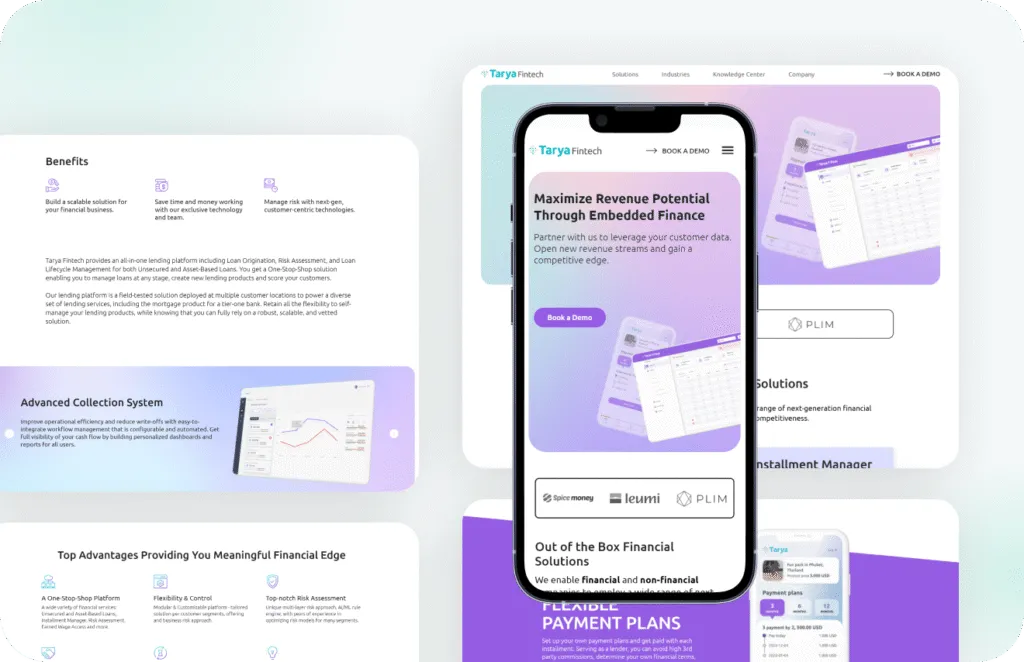
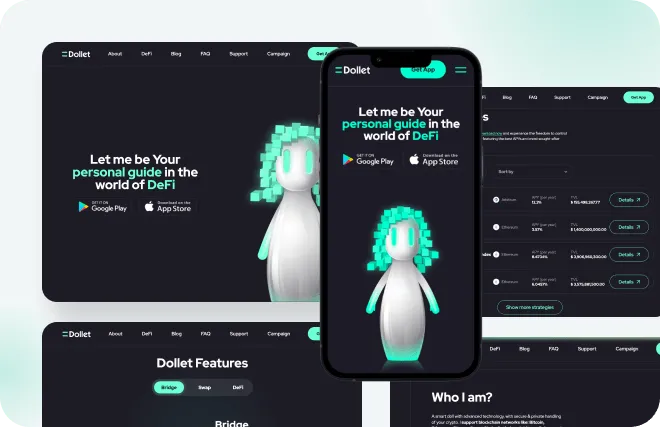
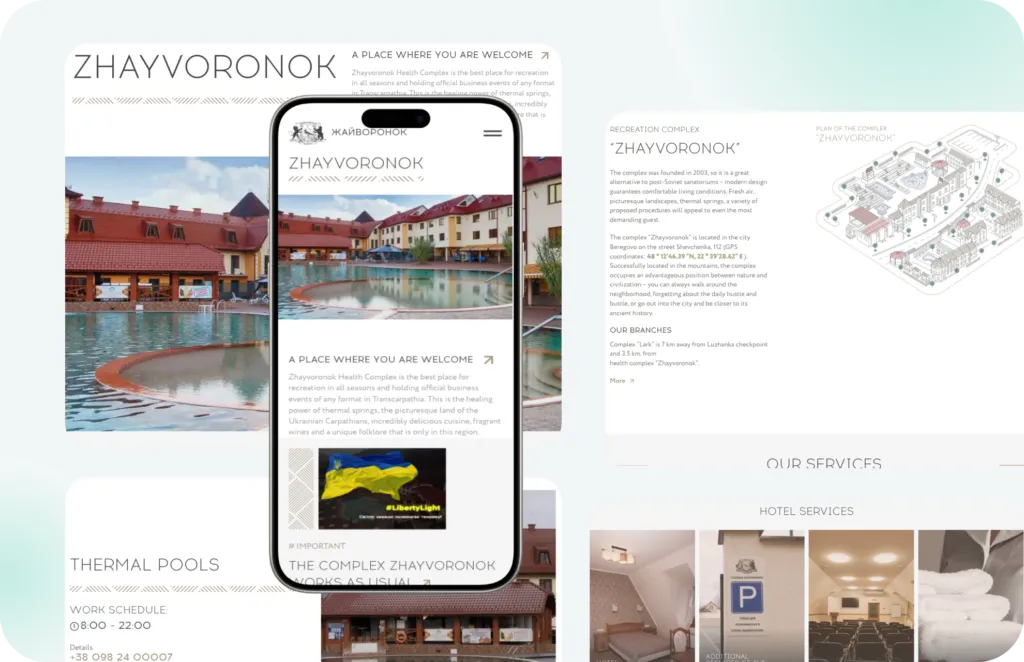
Stores we've built. Results
they've driven.
What our clients say

Why Artilab for WooCommerce security
We read code, not only scan it
WooCommerce context
Fixes without breaking sales
Reports you can act on
Security FAQ
What store owners ask about security work.
What does a WooCommerce security audit include?
A check of plugins, themes, custom code, user access, server settings, checkout scripts and backups. You get a report with each risk ranked and an estimate to fix it.
My store was hacked. Can you help now?
Yes. We isolate the site, remove malware, close the entry point and restore from a clean backup where possible, then run a full audit to prevent a repeat.
Will the audit slow down or break my store?
No. Scans and code review run on a staging copy, and we only need read access to the live site.
Is a security plugin like Wordfence enough?
A firewall plugin helps, but it does not fix vulnerable code or weak access. We set one up during hardening and fix the root causes too.
Does the audit make my store PCI compliant?
It does not certify compliance, but it checks what matters for WooCommerce, such as card data handling and checkout scripts. With hosted payment fields, your PCI scope stays small.
How often should a store be audited?
Once a year, and after any big change such as a redesign, a new payment gateway or a major new plugin.
